| oidf-structure | October 2026 | |
| Lindström | Informational | [Page] |
The Sweden Connect identity federation for OpenID Connect is built on OpenID Federation [OpenID.Federation] and profiled by the "Swedish OpenID Federation Deployment and Interoperability Profile" [OIDC.Sweden.Federation]. Sweden Connect declares federation rules and policies in "Sweden Connect – OpenID Federation Rules and Policies 1.0" [SC.Federation.Rules]. This document describes the Sweden Connect OpenID Federation structure and provides connection information for participating parties.
Sweden Connect is an identity federation operated by the Swedish Agency for Digital Government (Digg). It connects organizations that offer electronic identification services with organizations that need to authenticate the users of their services, so that a Relying Party can obtain authentication of a user from an OpenID Provider that Digg has approved, without having to establish a separate relationship with each individual provider.
The federation is built upon OpenID Federation 1.0 [OpenID.Federation], and profiled by the "Swedish OpenID Federation Deployment and Interoperability Profile" [OIDC.Sweden.Federation]. Sweden Connect declares federation rules and policies in "Sweden Connect – OpenID Federation Rules and Policies 1.0" [SC.Federation.Rules].
OpenID Federation gives the federation a common root of trust, the Trust Anchor, whose federation key every participant configures. Starting from that root, trust in an individual Entity is established by collecting and validating a chain of signed Entity Statements, and the metadata that a participant needs in order to interact with that Entity is carried in the same chain. Approvals that an Entity holds, such as the levels of assurance an OpenID Provider may issue tokens under, are expressed as Trust Marks. Registration and metadata discovery are in this way automated, so that participants do not need to exchange configuration out of band.
Registering an Entity in the Production or QA environments requires that the organization has a contract or an agreement with Digg. The Sandbox environment carries no such requirement, and is open to any organization that wants to test or develop against the federation. See Sweden Connect Federation Environments for the environments themselves, and Section 5.2.2, "Contract Trust Marks" of [SC.Federation.Rules] for how a signed contract is reflected within the federation.
This document describes how the Sweden Connect OpenID Connect federation is put together, and provides the information a party needs in order to connect to it. It does not itself define protocol requirements; those are found in the profiles it references. The intended audience is organizations that are joining, or have joined, the Sweden Connect OpenID Connect federation, together with the developers and operators of their Relying Parties and OpenID Providers.
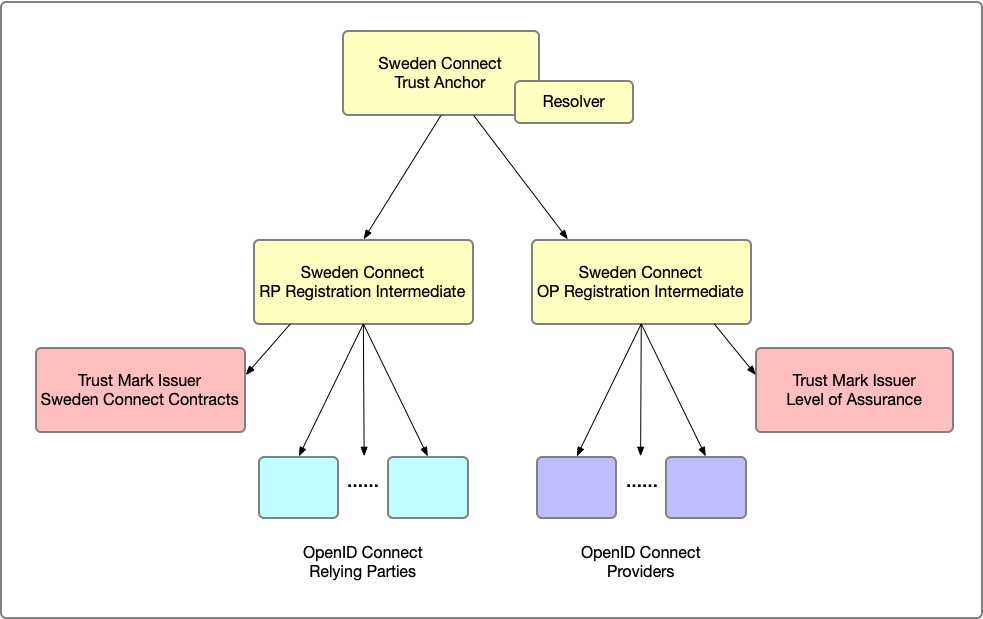
The reader will find the Entities that act as federation services within the federation, and the role each of them has, in Federation Structure. How a Relying Party or an OpenID Provider is registered is described in Joining the Federation, and the Trust Mark types defined for the federation are documented in Trust Marks. Finally, Sweden Connect Federation Environments gives the Entity Identifiers, endpoints, and Trust Anchor keys for each of the environments.
This document uses the terms "OpenID Provider (OP)" and "Relying Party (RP)" as defined by OpenID Connect Core 1.0 [OpenID.Core], and the terms "Entity", "Entity Configuration, "Subordinate Statement", "Intermediate Entity", "Subordinate Entity", "Superior Entity", "Trust Anchor", "Trust Mark", and "Trust Mark Issuer" defined in OpenID Federation 1.0 [OpenID.Federation].
The Sweden Connect OpenID Federation structure can be visualized as shown below:
An organization that has signed any of the contracts that give access to Sweden Connect can join the federation. No contract is required to join the Sandbox federation, see Section 3.1, Joining the Sandbox Federation, below.
During contract signing, each organization appoints one or more administrators who are given the right to log in to the Sweden Connect Metadata Registration Portal. An administrator uses the portal to administer the Entities of its organization.
The portal is accessible from:
A Relying Party can join in one of two ways:
An OpenID Provider can only join the federation by providing its Entity Identifier, from which its published Entity Configuration can be retrieved.
Note: The Sweden Connect Registration Intermediates check the parties that join the federation. This includes manual checks of display names and similar metadata parameters, and automated checks that verify compliance with the underlying standards.
An organization joins the Sweden Connect Sandbox federation by:
Read more about the Sandbox federation at https://sandbox.swedenconnect.se.
Section 5.2 of [SC.Federation.Rules] specifies the Trust Marks that are defined within the Sweden Connect federation.
This section provides information about the different Sweden Connect environments.
https://fed.swedenconnect.se/trustanchorhttps://fed.swedenconnect.se/trustanchor/resolveTrust Anchor Federation Key:
See Section 5.2.1 of [SC.Federation.Rules].
See Section 5.2.2 of [SC.Federation.Rules].
https://qa.fed.swedenconnect.se/trustanchorhttps://qa.fed.swedenconnect.se/trustanchor/resolveTrust Anchor Federation Key:
As PEM-encoded key file:
-----BEGIN PUBLIC KEY-----
MIGbMBAGByqGSM49AgEGBSuBBAAjA4GGAAQA0aliFcJ5cpnNjTz87tX6jLdoKTFr
bjLiiwGNBCJrDJWUpPcZtQ36yIXBUqu9p3oe7Og1LZD1kIjIht+myoIlLScA90D5
1nGPdiEsLJlXGgXNsEbhLCOFOul29PcCLp0Vw/t2EpvSVfBXIsa1GigOSKt68iF7
7Ep5V/gWjmlyvYs+2uQ=
-----END PUBLIC KEY-----

As JWK:
{
  "crv": "P-521",
  "kty": "EC",
  "x": "ANGpYhXCeXKZzY08_O7V-oy3aCkxa24y4osBjQQiawyVlKT3GbUN-siFwVKrvad6HuzoNS2Q9ZCIyIbfpsqCJS0n",
  "y": "APdA-dZxj3YhLCyZVxoFzbBG4SwjhTrpdvT3Ai6dFcP7dhKb0lXwVyLGtRooDkirevIhe-xKeVf4Fo5pcr2LPtrk",
  "kid": "CikQYhQZ3WOsSIjLC2E6yhzgOJHfg0suePny60V2Xfs",
  "alg": "ES512",
  "use": "sig"
}

As PEM-encoded X.509 certificate:
-----BEGIN CERTIFICATE-----
MIICCDCCAWmgAwIBAgIUc82lOuDXQzjP469OkjwBntUig6wwCgYIKoZIzj0EAwIw
QDELMAkGA1UEBhMCU0UxFzAVBgNVBAoMDlN3ZWRlbiBDb25uZWN0MRgwFgYDVQQD
DA9RQSBUcnVzdCBBbmNob3IwHhcNMjYwNjE3MTAzMTA5WhcNNDYwNjE3MTAzMTA5
WjBAMQswCQYDVQQGEwJTRTEXMBUGA1UECgwOU3dlZGVuIENvbm5lY3QxGDAWBgNV
BAMMD1FBIFRydXN0IEFuY2hvcjCBmzAQBgcqhkjOPQIBBgUrgQQAIwOBhgAEANGp
YhXCeXKZzY08/O7V+oy3aCkxa24y4osBjQQiawyVlKT3GbUN+siFwVKrvad6Huzo
NS2Q9ZCIyIbfpsqCJS0nAPdA+dZxj3YhLCyZVxoFzbBG4SwjhTrpdvT3Ai6dFcP7
dhKb0lXwVyLGtRooDkirevIhe+xKeVf4Fo5pcr2LPtrkMAoGCCqGSM49BAMCA4GM
ADCBiAJCAXzzLJpLhiwd13cITm3UEmbDS74zI9p55q0reME8VY/nit4f2U4EbwyT
8Md1OVWorflf7ajh6mCnlSSbn6+j840eAkIBqXnuoH3vrZuUycO/clrYb0UNPByY
ogmRYB1V92oqa8iVh1lo9Kum917vyqqtCalNP7X4dHOdhsOQlfU7wGXEiQw=
-----END CERTIFICATE-----

See Section 5.2.1 of [SC.Federation.Rules].
See Section 5.2.2 of [SC.Federation.Rules].
https://fed.sandbox.swedenconnect.se/trustanchorhttps://fed.sandbox.swedenconnect.se/trustanchor/resolveTrust Anchor Federation Key:
As PEM-encoded key file:
-----BEGIN PUBLIC KEY-----
MIGbMBAGByqGSM49AgEGBSuBBAAjA4GGAAQAythak2N9X+iWmumBTIpVyfxnFk5T
LFMyBe6SrKj6ZXaY3KSZpN25nsneEtGZsJACmo8cC7iCHvkJY8dJge44yQUBCk97
K3liYsy1/BYYQ4YZIqGo9ZAEhb4Fshb0qMnjgqzXjjF0BFIfwRfdZ50eo+kl9H/o
F8Lhw1F3eNYbZsY9dp8=
-----END PUBLIC KEY-----

As JWK:
{
  "crv": "P-521",
  "kty": "EC",
  "x": "AMrYWpNjfV_olprpgUyKVcn8ZxZOUyxTMgXukqyo-mV2mNykmaTduZ7J3hLRmbCQApqPHAu4gh75CWPHSYHuOMkF",
  "y": "AQpPeyt5YmLMtfwWGEOGGSKhqPWQBIW-BbIW9KjJ44Ks144xdARSH8EX3WedHqPpJfR_6BfC4cNRd3jWG2bGPXaf",
  "kid": "x8vWKOCUciPdbte5wyXkY4404TSwi8cok3Zrfj-f7PQ",
  "alg": "ES512",
  "use": "sig"
}

As PEM-encoded X.509 certificate:
-----BEGIN CERTIFICATE-----
MIICEjCCAXOgAwIBAgIUdRPcpnV3mGKmcK7r0ZgBnA5WnWswCgYIKoZIzj0EAwIw
RTELMAkGA1UEBhMCU0UxFzAVBgNVBAoMDlN3ZWRlbiBDb25uZWN0MR0wGwYDVQQD
DBRTYW5kYm94IFRydXN0IEFuY2hvcjAeFw0yNjAxMzAwOTU4MDNaFw0zNjAxMzAw
OTU4MDNaMEUxCzAJBgNVBAYTAlNFMRcwFQYDVQQKDA5Td2VkZW4gQ29ubmVjdDEd
MBsGA1UEAwwUU2FuZGJveCBUcnVzdCBBbmNob3IwgZswEAYHKoZIzj0CAQYFK4EE
ACMDgYYABADK2FqTY31f6Jaa6YFMilXJ/GcWTlMsUzIF7pKsqPpldpjcpJmk3bme
yd4S0ZmwkAKajxwLuIIe+Qljx0mB7jjJBQEKT3sreWJizLX8FhhDhhkioaj1kASF
vgWyFvSoyeOCrNeOMXQEUh/BF91nnR6j6SX0f+gXwuHDUXd41htmxj12nzAKBggq
hkjOPQQDAgOBjAAwgYgCQgFX0+3h5IvfN6pb+1xEVrpept3a64mjg+apgMRRtvBg
i91yP4yJ1YhMEtrd6OdY9WSsTTYIu1vIrHLcJLGGtn4x4wJCAPaUg1+vBh3y7Z9M
n6xpVgkeur9oX0Orc9zTloZqMjLPC0m2qx+mYwQrCzd97T++AqbWVKLe1/mqF+JD
WdHa51qR
-----END CERTIFICATE-----

See Section 5.2.1 of [SC.Federation.Rules].
See Section 5.2.2 of [SC.Federation.Rules].
Copyright (c) The Swedish Agency for Digital Government (Digg), 2015-2026. All Rights Reserved.
kid values for Trust Anchor JWKs for Sandbox and QA.